Cybersecurity, IT &
AI Insights
Practical guidance on security threats, compliance obligations, managed IT, and AI governance — written for Greater Sacramento organizations, not security researchers.

How Session Hijacking Bypasses MFA in Business Accounts
When a business discovers that an email account was compromised, one of the first things the owner says is: “We […]
Enterprise AI Usage Limits Push Employees to Personal Tools
Most organizations address shadow AI by focusing on employees who deliberately choose unauthorized tools. Usage limits introduce another path. When […]
Shadow AI Is Already Inside Your Organization
Employees may already be using AI tools your organization hasn’t approved or may not know about. The Verizon 2026 Data […]
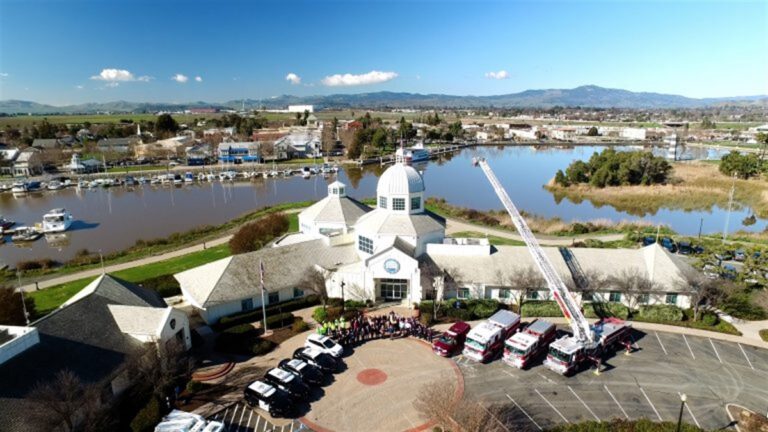
Suisun City Cyberattack: What Local Organizations Should Take from It
For Greater Sacramento organizations, this is a nearby example rather than a distant case study. On August 7, malicious software […]
Windows Server 2016 End of Support: What Greater Sacramento Businesses Need to Do Before 2027
Windows Server 2016 reaches the end of Microsoft’s extended support on January 12, 2027. After that date, standard security updates, […]
The HIPAA Security Rule May Be Changing. Here’s What Sacramento Healthcare Organizations Should Know.
The target window for finalizing the proposed HIPAA Security Rule has already passed. A final rule has not been published, […]